- The Most Effective Way to Normalise Surveillance Is to Call It Temporary
- Paris: The Temporary Exception
- From Exception to Infrastructure
- What Is Mission Creep?
- Datafication: When Ordinary Life Becomes Data
- The Legal Profession Is Not Outside This Problem
- Purpose Limitation Is a Discipline, Not a Checkbox
- The Surveillance Question for Law Firms
- The Danger of "It Already Exists"
- Build the Exit Before You Build the System
- Human Oversight Is Not Enough
- From Paris to the Legal Office
- Conclusion
The Most Effective Way to Normalise Surveillance Is to Call It Temporary
Exceptional powers rarely arrive announcing that they intend to become permanent.They arrive with a deadline.An emergency.A special event.A limited purpose.
The argument is reassuring:We only need this for now.
But the history of surveillance technology suggests a different question is more important:What happens when “temporary” technology proves useful?
Because once a system exists, the pressure to keep using it can become stronger than the original justification for introducing it.This is the problem of mission creep.
Paris: The Temporary Exception
For the 2024 Paris Olympics, France authorised the use of AI-assisted video surveillance to detect certain patterns in crowds, including abandoned objects, unusual movements, and other predefined events.The justification was exceptional circumstances.Millions of visitors.Large public gatherings.Heightened security requirements.
The technology was presented as a temporary measure connected to the Games, with the authorisation scheduled to expire in March 2025.The Olympics ended.But the technology did not simply disappear from the policy conversation.French authorities subsequently expressed interest in making elements of the approach more permanent.
That progression is precisely what makes temporary surveillance worth examining.
The original question is:“Is this necessary for the exceptional event?”
The question eventually becomes:“Why would we stop using something that appears to work?”
That is where the boundary begins to move.
From Exception to Infrastructure
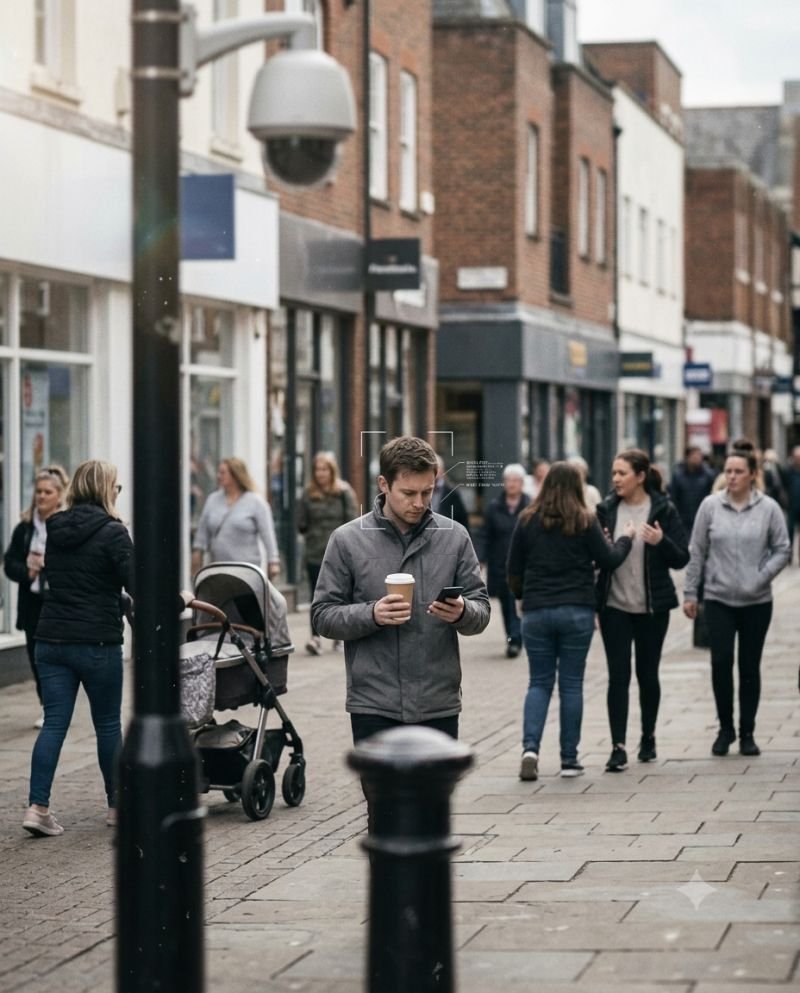
This pattern is not unique to France.The UK has experienced a similar evolution with facial recognition.In 2025, the Metropolitan Police introduced permanent live facial-recognition cameras in Croydon, moving beyond the temporary deployments that had previously characterised much of the technology’s use.
The difference is significant.A marked police van appearing at a particular event is visible and geographically limited.A camera permanently attached to the built environment is different.It becomes part of ordinary life.
The technology moves from:event → infrastructure
from:temporary → permanent
and eventually from:exception → expectation
That transition deserves scrutiny.
What Is Mission Creep?
Mission creep occurs when a technology, authority, or system gradually expands beyond the purpose for which it was originally introduced.The expansion does not necessarily happen through one dramatic decision.It happens incrementally.First, the system is introduced for a narrowly defined purpose.
Then another use appears.Then another.Each expansion seems reasonable on its own.Eventually, the original limitation becomes difficult to remember.The technology is no longer exceptional.It is simply there.That is what makes mission creep particularly difficult to detect.
There may never be a single moment when anyone consciously decides:“We are now normalising surveillance.”
Instead, normalisation happens one justification at a time.
Datafication: When Ordinary Life Becomes Data
Underneath mission creep is a broader transformation:datafication.
Datafication is the process through which ordinary human activity becomes something that can be captured, recorded, analysed, scored, and acted upon.Walking becomes movement data.Gathering becomes crowd data.Waiting becomes behavioural data.
Entering a building becomes an access record.A conversation becomes a transcript.A client inquiry becomes an intake dataset.Once behaviour becomes data, it can potentially be processed for purposes beyond the original interaction.
That is where governance becomes essential.
The Legal Profession Is Not Outside This Problem
Law firms may not operate facial-recognition systems in the same way as governments.But they are deeply involved in datafication.Consider a modern legal intake process.A prospective client visits a website.A chatbot starts a conversation.
The system records what they say.AI classifies the inquiry.The information enters a CRM.The system scores the lead.A follow-up is automatically generated.The interaction may be stored indefinitely.
Each individual step can appear harmless.Together, they create a detailed digital representation of the person seeking legal assistance.
The question is therefore not simply:“Are we allowed to collect this information?”
It is also:“Do we still have a legitimate reason to keep, analyse, and reuse it?”
Purpose Limitation Is a Discipline, Not a Checkbox
Responsible data governance requires organisations to define why information is being collected.That purpose matters.If a client provides information to determine whether a law firm can assist with a legal matter, that does not automatically mean the same information should become a permanent dataset for unrelated analytics, profiling, or AI training.
Purpose matters because data has a tendency to acquire new purposes.Information that was once collected for convenience can later become valuable for prediction.Information collected for prediction can later become valuable for automation.And information collected for automation can eventually become infrastructure.
That is how mission creep begins.
The Surveillance Question for Law Firms
Law firms should therefore ask a simple question whenever introducing an AI-enabled system:What are we collecting that we do not genuinely need?
Then ask:What will happen to it after the original purpose is finished?
And:Could this data later be used for a purpose that neither the client nor the firm originally contemplated?
These questions are particularly important where AI systems process:
- client communications;
- confidential documents;
- intake conversations;
- behavioural information;
- identity data;
- financial information;
- or sensitive personal information.
The fact that technology makes additional processing possible does not mean that additional processing is justified.
The Danger of “It Already Exists”
One of the most powerful drivers of mission creep is the existence of infrastructure.Once an organisation has invested in a system, removing it becomes politically, financially, and operationally difficult.The argument changes.
Initially:“Do we need this?”
Later:“We’ve already built it. Why wouldn’t we use it?”
That is a fundamentally different decision.The infrastructure itself begins to justify its continued existence.This is why limits must be designed before deployment.Not after the technology becomes embedded.
Build the Exit Before You Build the System
One of the most important principles of responsible AI governance is therefore surprisingly simple:Every exceptional system should have an exit strategy.
Before deployment, organisations should define:
- the precise purpose of the system;
- the legal basis for its use;
- the data it requires;
- the duration of deployment;
- who can access the information;
- what secondary uses are prohibited;
- when the system must be reviewed;
- and what conditions would require it to be discontinued.
A sunset clause is not bureaucracy.It is a governance mechanism against institutional inertia.
Human Oversight Is Not Enough
We often hear that human oversight will prevent AI systems from becoming dangerous.But human oversight itself can suffer from mission creep.A reviewer may initially assess whether a system is being used appropriately.Over time, familiarity develops.The system becomes trusted.The review becomes routine.
The exceptional becomes normal.This is why governance must include periodic reassessment, not simply approval at deployment.
The question should periodically return to its starting point:Would we authorise this system today if it did not already exist?
That is a powerful test.
From Paris to the Legal Office
The lesson from surveillance technology is not that every AI system will become a surveillance system.It is more fundamental.Technology creates possibilities faster than institutions create boundaries.Once a new capability exists, new uses will inevitably emerge.Some will be legitimate.Some will be useful.Some will be difficult to justify.
Good governance does not assume that technology will remain within its original boundaries automatically.It anticipates expansion.It establishes limits before expansion becomes normal.
Conclusion
Temporary powers have a tendency to become permanent capabilities.The technology introduced for an exceptional event can become infrastructure.The data collected for one purpose can become valuable for another.The system deployed as a pilot can eventually become part of ordinary life.That is mission creep.For governments, it raises profound questions about surveillance and civil liberties.
For regulated professions, it raises equally important questions about data, confidentiality, purpose limitation, and professional responsibility.The answer is not to reject technology.It is to design restraint into the system from the beginning.Define the purpose.Limit the data.Control secondary uses.Create meaningful review points.Build sunset mechanisms.
And most importantly, preserve the ability to say:“We no longer need this.”
Because the real test of responsible technology is not whether we can deploy it.It is whether we can choose not to use it once the original justification disappears.The exception should never become the rule simply because the infrastructure survived the emergency.
- AI Adoption Starts with Trust, Not Technology
- Why AI Adoption Fails in Law Firms: The Middle Management Bottleneck
- The Leadership Gap: Why AI Resistance at the Top Puts Law Firms at Risk
- The AI Copyright Reckoning: Who Owns Creativity in the Age of Generative AI?
- AI Hallucinations Are No Longer a New Problem. They Are Becoming a Professional Responsibility Problem.